

If your store sells to customers in both California and the European Union, you’re likely already navigating two of the most significant consumer privacy regulations in the world — and treating them as interchangeable is a mistake that can create real compliance gaps. California’s Consumer Privacy Act (CCPA) and the EU’s General Data Protection Regulation (GDPR) both aim to give individuals more control over their personal data, but they differ substantially in scope, requirements, and enforcement. In this article, we’ll break down the key CCPA vs GDPR differences, what each actually requires of ecommerce businesses, and how a privacy-compliant data collection strategy can help you meet both without treating compliance as two separate, disconnected projects.
What Is the Core Difference Between CCPA and GDPR?
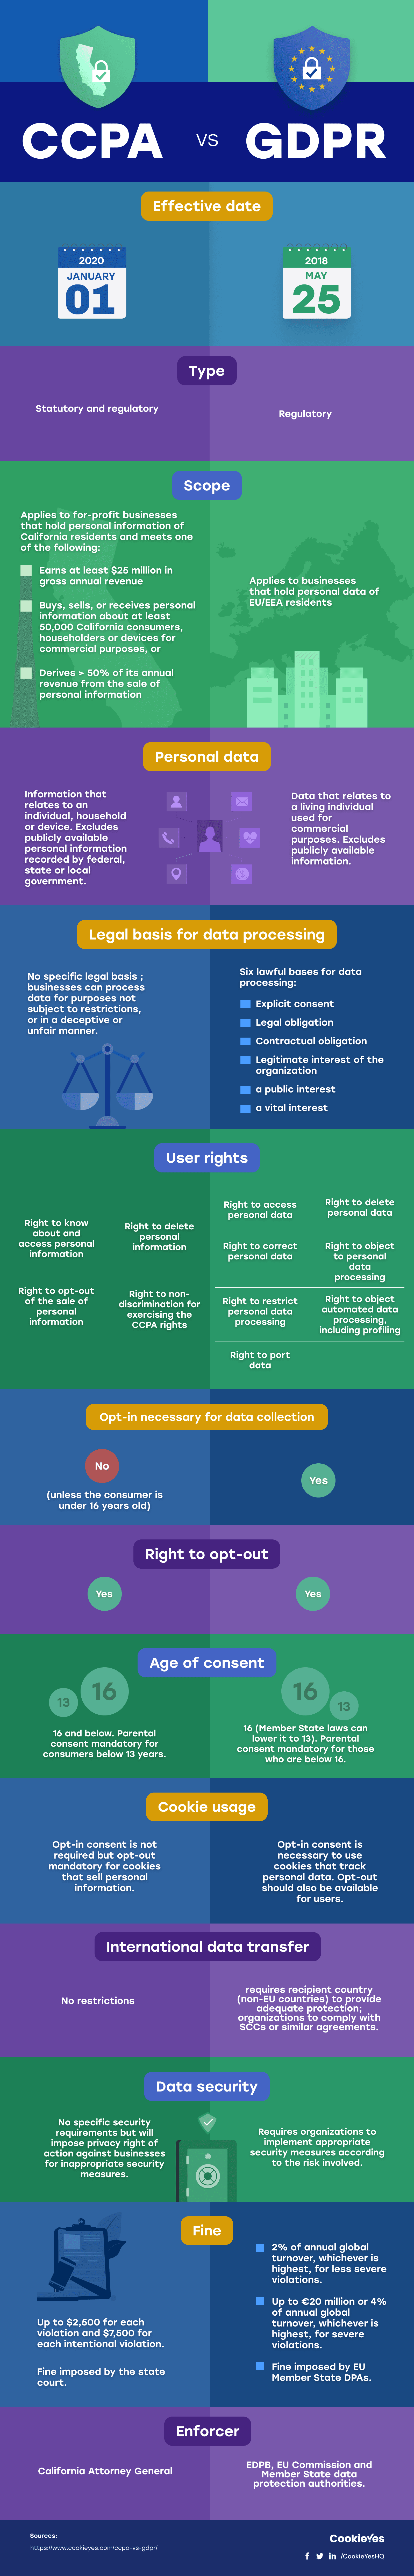
CCPA and GDPR share a common goal — giving individuals greater control over their personal data — but they differ fundamentally in legal structure, geographic scope, and default assumptions about data collection.
The core distinctions:
- Legal basis for data processing: GDPR requires an affirmative legal basis (most commonly explicit consent) before collecting or processing personal data; CCPA generally allows data collection by default, with consumers given the right to opt out rather than needing to opt in.
- Geographic and business scope: GDPR applies to any business processing the personal data of EU residents, regardless of where the business is located; CCPA applies specifically to for-profit businesses meeting certain revenue or data-volume thresholds that collect data from California residents.
- Definition of personal data: GDPR’s definition is broad and includes any information relating to an identified or identifiable natural person; CCPA’s definition is similarly broad but includes specific carve-outs and category-based definitions that differ in structure.
- Enforcement mechanism: GDPR is enforced by data protection authorities in each EU member state, with substantial fines tied to global revenue; CCPA (as amended by CPRA) is enforced by the California Privacy Protection Agency, with different penalty structures.
The practical consequence for ecommerce businesses is that GDPR’s opt-in default requires proactive consent collection before tracking or marketing to EU visitors, while CCPA’s opt-out model means US-based data collection can generally proceed by default, provided consumers are given a clear, accessible way to opt out and have their data-related rights respected when exercised. This structural difference alone significantly changes what a compliant WooCommerce checkout and marketing setup needs to look like depending on which regulation applies to a given customer.
Who Actually Needs to Comply With CCPA vs GDPR?
Determining which regulation applies to your business depends on where your customers are located and, in CCPA’s case, specific business-size thresholds — and many ecommerce brands selling internationally need to comply with both simultaneously.
GDPR applies to:
- Any business, regardless of location, that processes personal data of individuals residing in the EU or EEA, whether through direct sales, marketing, or monitoring of behavior.
- This extraterritorial scope means a WooCommerce store based entirely outside the EU can still fall under GDPR if it knowingly markets to or serves EU customers.
CCPA (and its amendment, CPRA) applies to for-profit businesses that:
- Have annual gross revenues exceeding a specified threshold, or
- Buy, sell, or share personal information of a specified number of California consumers or households annually, or
- Derive a specified percentage of annual revenue from selling or sharing California consumers’ personal information.
The common misconception is assuming a business’s physical location determines which regulation applies. In reality, both regulations are structured around where the customer is located, not where the business operates — meaning a small WooCommerce store based in Europe selling to a handful of California customers, or a US-based store with any EU traffic, may need to consider compliance obligations under both frameworks depending on scale and specific data practices, regardless of where the company itself is headquartered.
What Consumer Rights Differ Between CCPA and GDPR?
Both regulations grant individuals rights over their personal data, but the specific rights, how they’re exercised, and their scope differ in ways that directly affect how an ecommerce business needs to structure its data request processes.
Rights present in both frameworks, with differing scope:
- Right to access: both allow individuals to request what personal data a business holds about them, though GDPR’s access right is generally broader in scope and detail requirements.
- Right to deletion: both provide a deletion right, though GDPR’s “right to erasure” includes more specific conditions and exceptions than CCPA’s deletion right.
- Right to opt out of sale: CCPA explicitly grants a right to opt out of the sale (and under CPRA, sharing) of personal information; GDPR doesn’t use “sale” as a defined concept in the same way, since its consent-based model addresses this differently through the requirement for a lawful basis before processing occurs at all.
- Right to correction: both frameworks include a right to correct inaccurate personal data, though implementation specifics differ.
- Right to data portability: GDPR explicitly includes a right to receive personal data in a portable format; CPRA (CCPA’s amendment) introduced a similar right, though the specifics of implementation differ between the two.
The practical takeaway for ecommerce businesses is that a compliance framework built purely around one regulation’s rights structure often doesn’t fully satisfy the other — a request-handling process built solely for CCPA’s opt-out model, for instance, may not adequately cover GDPR’s broader consent-withdrawal and erasure requirements. Businesses serving both audiences typically need a data infrastructure flexible enough to honor the more stringent applicable right for each type of request, regardless of which regulation technically governs a given customer.
How Do Consent Requirements Differ for Marketing and Tracking?
Consent requirements represent one of the most operationally significant differences between the two regulations, directly affecting how a WooCommerce store’s cookie banners, email opt-ins, and tracking pixels need to be configured.
The key differences:
- GDPR requires opt-in consent before most tracking cookies (beyond strictly necessary ones) can be set, meaning EU visitors should see tracking blocked by default until they actively consent — a stricter standard than many US-based cookie banners are designed for.
- CCPA’s opt-out model means tracking and data collection can generally proceed by default for California visitors, with the business required to provide a clear “Do Not Sell or Share My Personal Information” mechanism rather than requiring upfront consent.
- Email marketing consent under GDPR generally requires explicit opt-in before adding someone to a marketing list; CCPA doesn’t impose the same opt-in requirement for email marketing specifically, though general data collection transparency obligations still apply.
- Granularity of consent: GDPR generally expects granular consent options (allowing a visitor to consent to analytics cookies but decline marketing cookies, for instance) rather than a single all-or-nothing toggle.
The common compliance mistake is deploying a single, US-style cookie banner globally and assuming it satisfies both regulations. A banner that only offers an opt-out mechanism doesn’t meet GDPR’s opt-in standard for EU visitors, while an overly restrictive default-blocked configuration built purely for GDPR compliance may unnecessarily limit legitimate CCPA-compliant tracking for US visitors who haven’t opted out. Effective compliance typically requires geo-aware consent configuration that applies the appropriate standard based on visitor location, rather than a single blanket approach.
How Can WooCommerce Stores Build a Compliance Strategy That Covers Both?
Rather than treating CCPA and GDPR compliance as two entirely separate projects, the most efficient approach is building a privacy-compliant data infrastructure flexible enough to satisfy the stricter applicable standard for each visitor, based on their actual location.
Practical steps for a unified approach:
- Implement geo-aware consent management, serving GDPR-compliant opt-in consent banners to EU visitors and CCPA-compliant opt-out mechanisms to California visitors, rather than a single global configuration.
- Build a centralized data request process capable of handling access, deletion, correction, and portability requests regardless of which regulation technically governs the requester, since building separate processes for each creates unnecessary operational complexity.
- Document data flows clearly, understanding exactly what personal data is collected, where it’s stored, and which third parties (ad platforms, email/SMS providers, analytics tools) receive it — a prerequisite for responding accurately to any data request under either framework.
- Configure tracking and marketing tools to respect consent signals, ensuring pixels, tags, and email platforms actually honor opt-in/opt-out status rather than firing regardless of the visitor’s stated preference.
- Review third-party vendor compliance, since using an ad platform or email tool that doesn’t itself support proper consent handling can undermine an otherwise compliant setup.
For WooCommerce stores specifically, this typically means pairing a consent management platform with server-side tracking configured to respect consent status, rather than relying solely on client-side scripts that may fire before consent is captured. Building this once, as unified infrastructure, is considerably more sustainable than maintaining parallel, disconnected compliance systems for each regulation.
Ready to take your e-commerce to the next level?
If your retention efforts feel like they’re stalling revenue, or if you suspect your current tracking setup is either over-collecting data in ways that create compliance risk or under-collecting it in ways that hurt attribution accuracy, privacy compliance and marketing performance aren’t actually in conflict — they depend on the same underlying data infrastructure. Getting consent management right protects the business legally while also improving the quality of the first-party data feeding your marketing decisions.
This is exactly the kind of gap we help DTC and ecommerce brands close. As an extension of your in-house team, we build data-driven systems where consent management, advanced tracking, and CRM work together — so your compliance posture and your marketing data quality improve together, not at each other’s expense. If you want a clear, honest read on how your current setup handles CCPA and GDPR obligations, book a free marketing automation audit and get a data-driven, conversion-focused view of your privacy and tracking infrastructure.

Comments